

The South African Phishing Epidemic: Is Your Business The Next Target?
We recently discussed why even a CEO should not have global administrative rights. But the uncomfortable truth is that for many South African businesses, the threat is already inside the perimeter—it arrives directly in an employee’s inbox every single day.
Phishing is no longer just unconvincing "spam" filled with spelling errors. It has evolved into a highly weaponized tool for corporate espionage, financial theft, and ransomware deployment. Because South African enterprises bridge advanced financial infrastructure with varying levels of security maturity, our local market has become a primary target for global cybercriminal syndicates. Local organizations now face over 2,200 cyberattacks every week, representing a relentless 22% increase year-on-year.
The Human Attack Surface
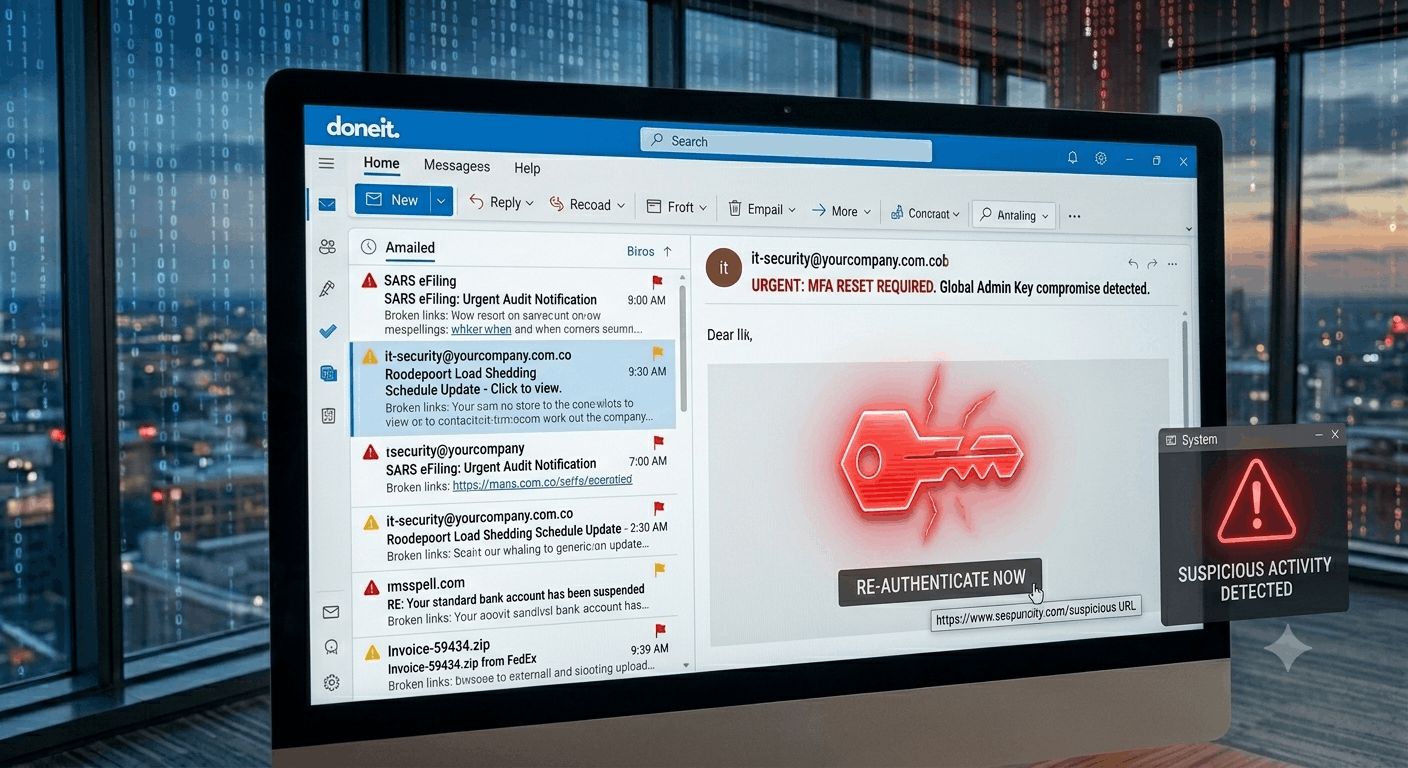
Why do sophisticated hackers still rely on techniques developed decades ago? Because breaking human psychology is far easier than cracking enterprise-grade encryption. Despite multi-million Rand investments in perimeter firewalls and endpoint security, the weakest link in the digital chain remains the "Human Attack Surface."
Your employees—spanning from front-desk receptionists to senior financial controllers—handle massive amounts of communication under tight deadlines. Attackers exploit this fast-paced operational environment through highly targeted variants of social engineering:
- Business Email Compromise (BEC): Cybercriminals spoof or hack an executive's account to send urgent, seemingly legitimate financial requests to accounts payable.
- Spear Phishing: Highly customized emails tailored with specific local information gathered from corporate public profiles and LinkedIn data.
- Whaling: Phishing attacks designed exclusively to target high-profile executives, aiming to steal high-level credentials that grant deep access to proprietary intellectual property.
Anatomy of a South African Phishing Scam
Modern localized phishing attempts are designed to mimic organizations your business interacts with daily. We regularly see campaigns engineered to look like legitimate alerts from:
- SARS eFiling Notifications: Fake tax compliance audits or urgent "refund pending" notices that steal corporate banking details.
- Eskom Load Shedding Adjustments: Malicious attachments disguised as "updated scheduling spreadsheets" or emergency power-grid updates.
- Bank Verifications: Urgent notifications mimicking major local banks (FNB, Standard Bank, Nedbank, Absa) demanding immediate credential validation to prevent corporate account suspension.
The Compliance Nightmare: Beyond Financial Loss
In South Africa, a successful phishing attack doesn't just impact your bank account; it triggers severe regulatory scrutiny. If an employee clicks a malicious link and exposes client information, your business is immediately in breach of the Protection of Personal Information Act (POPIA).
Failing to protect data assets due to inadequate security measures can result in administrative fines of up to R10 million, direct criminal liability, and permanent damage to your corporate reputation. If you don't actively train your staff to recognize these threats, your business could be found legally negligent.
Managed Awareness: The DoneIT Approach
Traditional "once-a-year" classroom style security training fails because the information is typically forgotten within weeks. Cyber threats evolve daily, which means your defensive posture must evolve just as quickly.
DoneIT provides a proactive, ongoing strategy. Instead of dull presentations, we deliver automated, simulated phishing attacks designed specifically around real-world South African threat vectors. We test your staff safely, showing them exactly where they fell short, and tracking improvement metrics over time. This continuous feedback loop transforms your workforce from an operational vulnerability into an active Human Firewall.
A Multi-Layered Defense Formula
We believe that security is an organizational culture that starts with behavioral training and is enforced by modern access protocols. Building a resilient business requires:
- Continuous security awareness training.
- Robust Email Gateway filtering to stop threats before they reach the inbox.
- Strict Multi-Factor Authentication (MFA) to render stolen passwords useless.
Are you ready to arm your team against the region's fastest-growing digital threat? Learn more about our managed security training and technical IT solutions here.